The Digital Handoff That Prevents Expensive Injection Mold Revisions

Injection molding projects rarely fail because a team forgot to send a CAD file. They fail because the file travels without the decisions that give it meaning. Procurement quotes one revision, engineering comments on another, the toolmaker solves a gate or ejection problem in a meeting, and quality receives a sample without knowing which temporary conditions produced it.

A digital handoff is not a shared folder full of attachments. It is a controlled record that connects product requirements, DFM decisions, tool design, sampling evidence, and approval. Small manufacturing teams can build that record without deploying a complex enterprise system, but they must agree on ownership and status.
Chain-locked book, phone, and laptop symbolizing digital and intellectual security.

Give Every Release One Identity

The project should have one released product definition at a time. That release can include the 3D model, drawing, material specification, appearance standard, critical dimensions, assembly context, and expected quantity. Give the package a revision and date, then make superseded packages visibly obsolete.

Avoid filenames such as “final,” “latest,” or “new.” They describe a sender’s belief, not a controlled state. Use a consistent part number, revision, and document type. If the drawing and model differ, define which one governs each kind of requirement and resolve conflicts before tooling work continues.

The release should also name an engineering owner. A supplier needs one route for questions when different stakeholders give incompatible answers.

Capture DFM Decisions as Structured Records

DFM feedback often arrives as screenshots, slides, or chat messages. Those formats are useful for discussion but weak for approval. Convert each open item into a short record containing:

  • Feature or location
  • Manufacturing concern
  • Supplier recommendation
  • Product or assembly impact
  • Decision owner
  • Due date
  • Approved answer
  • Affected files and revisions

A shared reference for the components of an injection mold helps teams name the affected insert, gate, ejector, cooling feature, or side action consistently. The log should also cover parting, draft, texture, and dimensions that depend on tool construction. The toolmaker should not have to infer whether silence means approval.

Number the records so that a tool-design review can reference a decision without restating it. Close an item only after the released files reflect the answer. Otherwise, the log and CAD will drift apart.

Separate Product Changes From Tool Responses

Product geometry and tool geometry are related but not identical. A product change may require a tool response, while a toolmaker may adjust steel or process conditions without changing the nominal part model. Track these paths separately.

A product change record should explain why the requirement changed and what validation must be repeated. A tool-change record should identify the affected insert or component, the purpose of the modification, the before-and-after condition, and the sample event that will verify it.

Build a Sample Event Package

Every sampling round should have a defined question. “See how the parts look” is not enough. State whether the event is checking filling, ejection, appearance, dimensions, assembly, a recent tool correction, or a combination of these.

The package should connect:

  • Tool revision and configuration
  • Product revision
  • Material identification
  • Machine and key process record
  • Temporary conditions or deviations
  • Sample quantity and selection method
  • Dimensional and functional results
  • Photos of relevant conditions
  • Open issues and next decision

Applied alongside practical injection molding design guidance, this record becomes the bridge between tool development and repeat manufacturing. The approved process should be traceable to the part that passed dimensional, cosmetic, and functional review.

Do not treat selected samples as the entire result. Record what happened across the event, including startup behavior, rejected parts, manual adjustments, and any feature that was difficult to stabilize.

Create One Approval Dashboard

Teams often confuse activity with progress. A dashboard should show the few gates that determine readiness rather than count messages or meetings. Useful statuses include:

  • Product definition released
  • DFM actions closed
  • Tool design approved
  • Tool manufacture complete
  • Sample event completed
  • Dimensional review approved
  • Appearance review approved
  • Functional assembly approved
  • Process conditions defined
  • Open deviations resolved
  • Production release authorized

Control Communication Across Email, Chat, and Meetings

Teams do not need to ban email or chat. They need a rule for promoting decisions into the official record. A practical rule is: discussion can happen anywhere, but an approval is valid only when recorded in the decision log or release system.

Notifications should point to the controlled item instead of carrying a second copy as an attachment. This reduces the chance that recipients download a file and keep working after it changes.

Protect the Handoff to Quality and Operations

Quality needs more than a drawing. It needs the approved sample context, critical-feature rationale, inspection method, conditioning requirements where relevant, and the disposition of known cosmetic conditions. Operations needs the released work instructions, process window, packaging method, maintenance expectations, and escalation path.

Schedule a formal handoff before the first production order. Review open deviations, temporary tooling, measurement disagreements, and manual work used during sampling. If an item remains unresolved, give it an owner and containment plan rather than allowing it to disappear into production.

Conclusion

A reliable digital handoff gives every decision a home and every release a traceable identity. It connects CAD, DFM, tool changes, samples, inspection, and production approval without requiring a large software deployment. Before the next tooling commitment, run a configuration audit and close any gap between the approved record and the files the supplier is using.

FAQ

Is a shared cloud folder enough for mold projects?

It can store files, but it does not automatically control revision, status, ownership, or approval. Add a release convention and decision log.

Who should approve DFM changes?

The product owner for the affected requirement should approve them with input from manufacturing, quality, sourcing, and assembly as needed.

Should process settings be included in sample reports?

Yes, at a level appropriate to the project. The team must know whether an approved sample represents a stable, repeatable process or an unusual temporary condition.

How can small teams avoid excessive administration?

Track only decision-relevant records, use templates, assign one owner per item, and link to controlled evidence instead of copying it.

What is the most important pre-production audit question?

Ask whether the released product, current tool, approved sample, inspection plan, and supplier instructions all refer to the same configuration.
A Buyer’s Checklist for Evaluating EHS Management Software

Environmental, health, and safety teams need clear records, timely hazard data, and dependable processes across worksites. A suitable platform should support those priorities while daily safety tasks remain clear and efficient. Buyers can make a stronger choice when each product is assessed against practical needs and compliance duties.

A well-selected EHS software platform can place safety records, inspections, incidents, and corrective actions in one system. The best evaluation starts with the work employees must complete each day, and the information leaders need for sound decisions. This checklist explains the core factors buyers should review before they select a platform for long-term use.

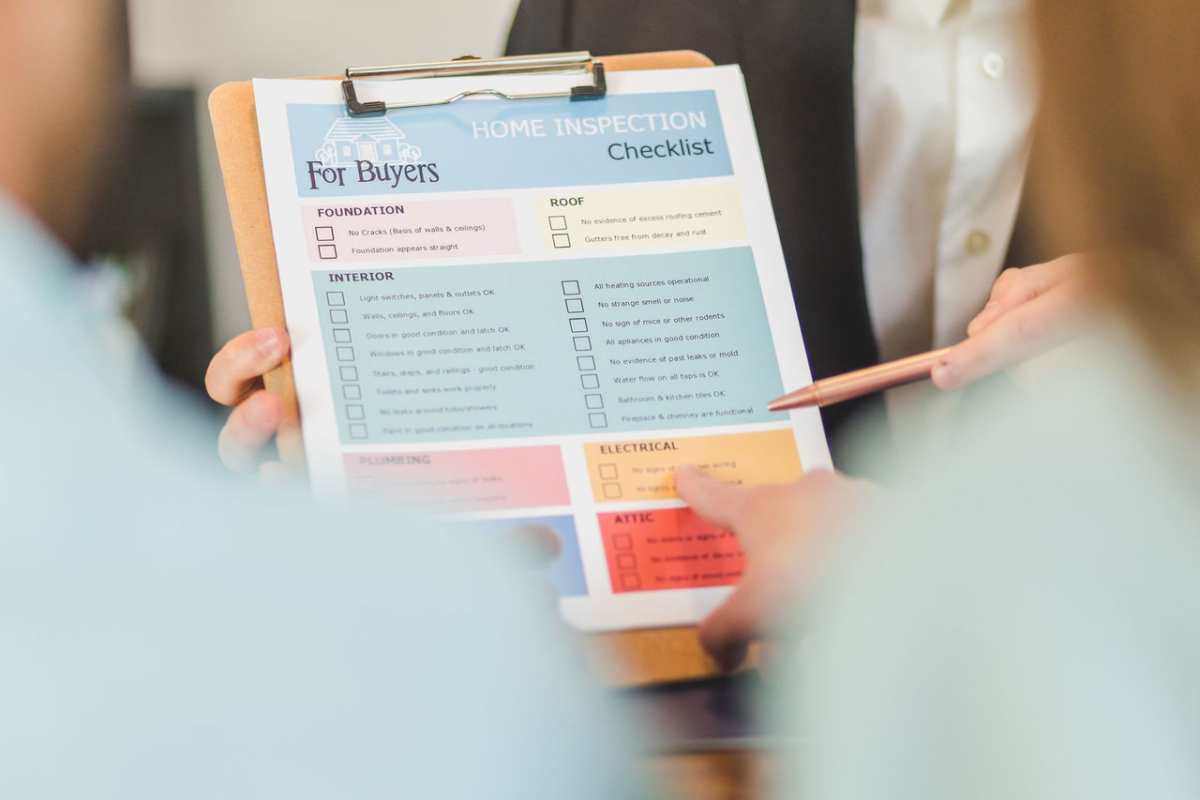
Close-up of hands holding a home inspection checklist clipboard for buyers.

Match the Platform to Core Safety Tasks

Incident and Hazard Records

The system should let teams capture incidents, near misses, hazards, and related details through structured forms. Buyers should confirm that records can connect to follow-up actions, responsible staff, due dates, and documents. This structure helps teams preserve context from the first report through final resolution.

Inspections and Corrective Actions

Inspection tools should support standard checklists, custom forms, schedules, findings, and action assignments across sites. Corrective action features should provide ownership, priority, status, and closure records so unresolved issues stay visible. These functions help create a consistent process for reviews and audits.

Review Compliance and Record Controls

Regulatory records deserve close attention because incomplete documentation can weaken safety oversight. The U.S. Bureau of Labor Statistics reported 2.5 million nonfatal workplace injuries and illnesses among private-industry employers in 2024. Buyers should check for OSHA record support, audit-ready reports, secure document storage, and clear historical records.

Test Data Access and Practical Use

Dashboards and Reports

Useful dashboards should present trends, open actions, incident data, inspection results, and key safety measures without complex manual steps. Reports should offer filters for site, date, event type, department, or other useful fields. Clear access to this data can help leaders spot repeat concerns and set priorities from evidence.

Mobile and Field Access

Field users may need to enter inspection or incident details away from a desk, so mobile access deserves careful review. Buyers should test form access, photo capture, offline capability, synchronization, and ease of use on common devices. A simple field process supports timely records and reduces gaps between an event and its formal documentation.

Assess Configuration and Workflow Fit

Every organization has different forms, approval paths, risk criteria, and site structures, so rigid software can create extra work. Buyers should review configurable forms, role permissions, alerts, task rules, risk matrices, and data fields before a decision. The goal is a system that fits established safety processes with room for sensible process updates as needs change.

Examine the Full Product Scope

A comprehensive platform can unite incident records, inspections, hazards, corrective actions, OSHA forms, analytics, and mobile field tools in one system. Some products also connect safety events to assigned courses or follow-up tasks, which can support a complete response after an incident or audit. These capabilities closely reflect the client product’s scope, which includes incidents, inspections, corrective actions, hazards, dashboards, OSHA compliance tools, mobile access, and configurable forms.

Confirm Long-Term Value Before Purchase

Price matters, but buyers should also review implementation support, user permissions, data migration, scalability, security, and future administration. The right ehs software should give safety teams a practical structure for consistent records, timely action, and reliable oversight across locations. A final review with safety, operations, IT, and compliance stakeholders can expose gaps before a contract is signed.

A careful software review starts with real safety tasks, regulatory duties, data needs, and user workflows. Buyers should favor clear functionality, flexible controls, dependable records, and practical access over features that add little operational value. A structured checklist makes it easier to compare platforms on the factors that can support safer and more accountable EHS processes.

AI Agents Turn Everyday Integrations Into Privileged Automation

Small businesses already rely on automation to move information between email, calendars, CRM systems, accounting tools, cloud storage, and customer databases. AI agents change the risk profile because they can decide which integration to use, interpret unstructured instructions, and take several actions in sequence without a person approving every step. The security issue is not that these integrations suddenly become malicious. It is that ordinary productivity connections can become privileged automation. A token created to make work convenient may give an agent enough authority to read contacts, send messages, update records, or access files at machine speed.

Two cheerful call center agents at work, engaging with customers and providing support.

The permission behind the integration matters more than the interface

AI assistants often look harmless because users interact through a chat box. The visible interface can obscure the authority behind it. What matters is the authority hidden behind that interface.

An agent connected to email may be able to read messages and send as the user. A CRM integration may permit contact updates or deal changes. Calendar access can expose customer names, travel plans, and meeting details. File access can include far more than the document relevant to the current request.

Security teams should therefore evaluate an agent by its effective permissions, not by how simple the user experience appears. The right question is: if the agent were manipulated or made a bad decision, what could the credentials attached to it actually change? Effective permissions are a more reliable measure of agent risk.

OAuth scopes are a security architecture decision

OAuth makes integrations easier because users can grant access without handing over a password. The integration's security still depends on which scopes are requested and how long the resulting token remains usable. Scope design is therefore part of the threat model, not merely an integration detail.

Broad scopes are convenient during development. They also create durable authority. An agent that only needs to read a customer’s contact record should not automatically receive permission to delete records, export an entire database, or modify account settings.

This is where small implementation choices matter. Request the narrowest scope, separate read and write capabilities where possible, avoid shared credentials, and use short-lived access when the platform supports it. Permissions should reflect the current workflow rather than every action the application might someday perform.

NIST’s 2026 concept paper on software and AI agent identity and authorization highlights this emerging challenge directly: agents need stronger approaches to identity, authorization, and delegated access as they begin acting across systems. The important implication for everyday business software is that agent permissions should be treated as first-class security objects, not hidden configuration behind a connector. Delegated access should be visible and reviewable like any other privileged permission.

AI agent security starts with separating suggestion from execution

For a broader definition of the topic, this glossary page on AI agent security provides an overview of the security considerations around autonomous agents. A useful design pattern is to let the model propose an action while trusted application logic decides whether that action can execute. The distinction sounds small but creates a meaningful control boundary. The model can suggest sending an email, modifying a customer record, or moving a file. Before execution, the application checks the authenticated user, target resource, requested operation, data involved, and relevant policy. High-impact actions can require a confirmation step.

This is one of the most practical ideas in AI agent security: the model should not be able to enlarge its own authority simply by generating a convincing instruction. Business rules should live outside the conversation in code or policy the model cannot rewrite. That keeps business policy outside the model’s own reasoning loop.

Long-lived tokens outlive the task that justified them

A user might ask an agent to perform a five-minute task while the underlying token remains valid for weeks or months. That mismatch creates unnecessary exposure. If a browser extension, local machine, automation service, or agent runtime is compromised later, the attacker may inherit permissions that were originally granted for a task long since completed. The user remembers approving one workflow; the credential silently remains available for many more.

Short-lived credentials reduce that gap. Where temporary credentials are not available, businesses should at least review connected applications, revoke unused grants, and separate sensitive integrations from general-purpose assistants. A discussion of privileged access management makes a related point: access becomes safer when trust is tied to verifiable proof, shorter trust periods, and clearer records rather than reusable credentials that persist indefinitely. AI agents increase the value of that model because machine-driven activity can amplify the consequences of one stolen credential.

Confirmation should depend on reversibility

Requiring approval for every agent action would eliminate much of the value of automation. Requiring approval for nothing creates the opposite problem. The control should scale with the consequence of the action.

A better approach is to classify actions by consequence. Reading an approved record may proceed automatically. Drafting a message can be low risk if a human still sends it. Sending to an external recipient, deleting information, changing payment details, or updating a large number of customer records should trigger stronger verification.

Reversibility is a useful design test. If an action can be easily undone and has limited external impact, automation can tolerate more autonomy. If the action is difficult to reverse, affects money, changes permissions, or communicates externally, the system should introduce an authorization breakpoint.

Agents need their own audit trail

Conventional application logs may show that a valid API request occurred. That is not enough to reconstruct an agent-driven workflow. A useful audit record should preserve who initiated the task, which agent acted, what system it accessed, what data category was involved, which action was proposed, whether confirmation was required, and which credential or delegated permission authorized execution.

This is especially important when one instruction creates several downstream actions. A request such as “prepare the customer for tomorrow’s meeting” could cause an agent to retrieve a CRM record, read email, inspect a calendar, summarize documents, and draft a message. The organization needs one traceable task chain, not five disconnected logs.

Small businesses need fewer permanent permissions

Large enterprises can build dedicated identity teams and complex policy infrastructure. Small businesses need a simpler principle: reduce how much permanent authority is attached to automation. Use separate service identities for sensitive workflows, minimize scopes, avoid sharing integration accounts, review inactive connections, keep high-impact actions behind confirmation, and expire access whenever the task no longer needs it. These controls reduce risk without preventing employees from using automation productively.

Real estate agent discussing property details with client using a clipboard indoors.

The core challenge is not whether AI agents can be trusted in the abstract. It is whether the surrounding software architecture gives them only the authority required for the job. As agents become embedded in ordinary productivity tools, integration security will increasingly determine AI security. The safest agent is not necessarily the one with the longest list of behavioral rules. It is the one whose permissions are narrow enough that an unexpected decision cannot silently become an unlimited business action.

Key Steps to Take After a Felony DUI Arrest in Cocoa Beach

A felony DUI arrest in Cocoa Beach can create immediate legal challenges that require careful decisions from the very beginning. Every action after the arrest may affect court proceedings, driving privileges, and future legal options. A clear understanding of the next steps helps protect important rights while reducing avoidable mistakes.

The first priority should be obtaining legal guidance from a felony DUI attorney in Cocoa Beach as early as possible. Florida felony DUI cases may involve repeat offenses, serious bodily injury, or other aggravating circumstances that carry substantial penalties under state law. Prompt legal review allows the facts, evidence, and procedural details to receive careful examination before the case moves forward.

Flat lay of a colorful desktop featuring a notebook, eyeglasses, and house key with numbers scattered.

Protect Legal Rights Immediately

Avoid discussing the incident with friends, coworkers, or on social media after release. Statements made outside the attorney-client relationship may later become evidence during the case. Careful communication helps preserve legal defenses while preventing unnecessary complications.

Keep Important Records Organized

Complete records allow legal counsel to review deadlines, identify missing information, and prepare an organized defense strategy. Collect and safely store documents connected to the arrest, including:

  • Citation or charging documents
  • Bond paperwork
  • Vehicle impound information
  • Court notices
  • Driver's license paperwork

Address Driver's License Issues Promptly

A DUI arrest may trigger administrative driver's license consequences that follow separate procedures from the criminal case. Certain deadlines may apply when seeking review of a suspension, making prompt action important. Early attention to licensing matters may help preserve available legal options before deadlines expire.

Follow Every Court Requirement

Missing court obligations can create additional legal problems beyond the original charge. Consistent compliance demonstrates respect for court procedures and helps prevent unnecessary setbacks. Stay prepared by:

  • Attending every scheduled court appearance
  • Following bond conditions carefully
  • Completing any court-ordered requirements on time
  • Keeping contact information current with legal counsel when appropriate

Review The Evidence Carefully

Every felony DUI case depends on its specific facts and the evidence collected during the investigation. A felony DUI attorney in Cocoa Beach can examine the legality of the traffic stop, field sobriety testing procedures, chemical testing methods, officer observations, and other evidence that may affect the prosecution's case. Careful analysis may reveal procedural issues or weaknesses that deserve further legal review.

Prepare For The Legal Process

Felony DUI cases may involve several stages before reaching a final resolution. According to the National Highway Traffic Safety Administration, more than 11,500 people per year, on average, died in drunk-driving crashes between 2015 and 2024, which supports the extensive legal procedures applied in these cases. These commonly include:

  • Initial hearings
  • Evidence review
  • Motion hearings
  • Negotiations when appropriate
  • Trial preparation if necessary

A felony DUI case in Cocoa Beach requires patience, organization, and careful attention to legal advice from start to finish. Keeping appointments, maintaining accurate records, and responding promptly to legal requests can support a smoother defense process. Early preparation and informed decisions place the case in a stronger position while protecting important legal rights throughout every stage.

Get Legal Guidance After A Felony DUI Arrest in Cocoa Beach

Legal guidance after a felony DUI arrest helps protect important rights while addressing court procedures, evidence review, and case deadlines. An attorney can evaluate the circumstances of the arrest, identify legal issues, and develop a defense strategy based on the facts of the case. Early legal support also helps reduce procedural mistakes that may affect the outcome.

A felony DUI case requires careful preparation from the first court appearance through the final resolution. Staying organized, following legal requirements, and making informed decisions can strengthen the defense process at every stage. Prompt action and qualified legal representation provide valuable support throughout the case.

How Square Footage Actually Shapes Your Startup Cost Plan (2026 Data)

Your rent line item might be the biggest number in your budget, but it is nowhere near the whole story. The square footage you lease quietly inflates nearly every other operating cost you will pay, from utilities to cleaning to coverage premiums. A 1,200 square foot space can cost you $3,000 more a year in insurance alone than a 400 square foot one. That gap only grows when you add in the bills nobody warns you about on day one. So before you sign that lease, you need to know exactly what every extra foot is actually charging you.

Here is the promise: by the end of this piece, you will know how to estimate your true monthly cost per square foot, spot the expenses that scale with your space, and decide whether that bigger office is worth it or just a slow drain on your runway. Let’s walk through the real numbers and the real math that most founders skip.

Why Square Footage Sneaks Into Every Line Item

Rent is the obvious one. But the second you commit to a physical space, you are signing up for a cascade of costs that all key off that same number. Utilities bill by the square foot, not by your headcount. Janitorial services quote by the square foot. Property damage coverage premiums scale with your insured area. Even your business personal property coverage often ends up tied to the footprint where that property sits.

Here is the thing: most startup cost templates only ask for rent, utilities, and maybe equipment. That leaves a gap big enough to drive a truck through. When I look at the budget breakdowns founders share online, the missing line items are almost always the ones tied directly to square footage.

The Bureau of Labor Statistics tracks this kind of thing carefully. Their 2019 report on business rents showed that leased commercial space made up roughly 4.5 percent of total operating expenses for the average American business. That figure predates the post-pandemic run-up, so current numbers run higher, but the structure of the cost is the same. Rent is not the anchor of your budget. It is one slice of a much larger square-footage-driven pie.

The Overhead Costs That Scale With Your Space

Let’s break down what actually moves when you add square footage. I am not listing these in order of importance, just in the order they will hit your bank account.

  • Utilities: Heating, cooling, and lighting a 2,000 square foot space costs roughly double what a 1,000 square foot space does. You cannot negotiate your way around physics.
  • Cleaning and maintenance: Janitorial companies charge by the square foot. Commercial cleaners in most metros quote between $0.10 and $0.20 per square foot per visit.
  • Property insurance: Commercial property coverage is priced off your building’s replacement value and your total insured area.
  • Liability coverage: Your general liability premium rises with your premises footprint because more space means more visitor traffic surface area.
  • Furniture and fixtures: Bigger rooms beg for more desks, more chairs, more storage. Nobody budgets for the second round of furniture, but it always comes.

Notice something? Four of those five costs are tied to the physical space itself, not to how many people work there. A team of five in 500 square feet pays meaningfully less than a team of five in 1,500 square feet, even though the headcount is identical.

How to Estimate Your True Cost Per Square Foot

You need a number that captures everything, not just rent. Here is the method I use when I talk to founders about their space. It takes ten minutes and it will save you from a nasty surprise in month six.

Step 1: Add up your annual rent, property taxes, and common area maintenance (CAM) fees. Divide by 12. That is your base occupancy cost per month.

Step 2: Estimate annual utilities at $2.50 to $3.50 per square foot. This is a solid planning range for typical office use in most U.S. markets.

Step 3: Add cleaning at $1.50 to $2.00 per square foot per year, assuming weekly service.

Step 4: Add insurance. This is where most people guess low, and it is exactly where you should get precise numbers rather than ballpark figures. Your small business insurance quote should list premises coverage separately so you can see what the footprint is actually costing you.

Step 5: Add furniture amortization. Take your total furniture budget and divide by 60 months (a reasonable five-year life). Add that to the monthly total.

Divide the whole thing by your square footage. That is your true monthly cost per square foot. In most U.S. metros it lands between $4 and $9 per square foot per month. If you are above $10, you had better be in a premium downtown location or running a revenue-generating retail operation.

What the Data Says About Space Utilization

The United States Census Bureau has been tracking how American businesses actually use their space. Their 2021 analysis of home-based businesses found that roughly half of American businesses operate from home, and those businesses reported substantially lower overhead costs as a share of revenue. The Census data showed office and other non-home-based businesses carried significantly higher expense ratios tied to physical premises.

That is not an argument against leasing. Some businesses need the space, full stop. Retail needs a storefront. Restaurants need a kitchen. Clinics need exam rooms. But the Census number tells you something important: if your business can operate from home, the cost savings are not marginal, they are structural. A home-based business in their data paid a fraction of the occupancy costs of a leased-space business with similar revenue.

When the Bigger Space Is Worth It

I am not going to tell you to shrink your footprint just to save a buck. There are legitimate reasons to lease more space than you strictly need right now.

Client-facing businesses signal credibility with a professional storefront or office. That signal can pay for itself in closed deals. A product-based business needs warehousing and packing space. A team that hates commuting will happily trade a bigger office for a shorter drive. Those are real benefits that show up in your revenue and retention numbers.

But here is my honest take: lease for what you need in year two, not what you hope for in year five. You can always expand. Breaking a lease early is expensive, and subletting empty space is a distraction that eats your time. The founders I have seen struggle with overhead are almost never the ones who under-leased. They are the ones who signed a beautiful 3,000 square foot space for a business that needed 1,200.

One caution: your coverage costs will not shrink just because you downsize. Some policies have minimum premiums, and liability coverage in certain industries starts at a base rate regardless of whether you are in 300 square feet or 3,000. So when you downsize, push your insurer for a revised quote rather than assuming the premium drops automatically.

Build the Space Budget Before You Tour

Do not walk into a property tour without a number in your head. Pick your maximum monthly occupancy cost first, then work backward to the square footage that fits. That single number will save you from falling in love with a space you cannot actually afford.

Here is the quick checklist I give every founder I talk to:

  • Set your maximum total monthly occupancy cost before you look at any property.
  • Request an insurance quote for each candidate space during your due diligence, not after you sign.
  • Ask the landlord for the last 12 months of utility bills for the unit.
  • Get a cleaning quote in writing before you negotiate the lease.
  • Build a 10 percent buffer into your occupancy line for the surprises that always show up.

The math is not glamorous, but it is simple. Every square foot you lease is a monthly payment to someone, and I mean every foot. The question is not whether you will pay for that space. It is whether you will price it into your plan before the invoices arrive, or discover it when the bank statement hits.

So what is your number? Run the calculation on your current space or your dream space, and see whether the footprint you have in mind matches the one your budget can actually carry.

The Small Business Software Stack: How to Choose Tools That Actually Earn Their Keep

Small businesses have never had access to better software.

A ten-person company can now use customer relationship management, automation, analytics, accounting and collaboration tools that would once have required an IT department and a substantial technology budget. The barrier to entry has collapsed, and in most cases that is a very good thing.

The problem is what happens next.

A CRM gets added because sales needs somewhere better to manage leads. The team adopts a project management platform. Marketing wants email automation. Customer support needs a shared inbox. Someone discovers an AI tool that cuts an hour from a weekly task. Before long, the business is paying for 15, 20 or 30 different products.

None of them looks particularly expensive on its own.

Together, they can become one of the company’s more significant operating expenses.

The answer is not to strip the software stack back to the cheapest possible collection of tools. Good software earns its keep. The challenge for a small business is working out which products genuinely make the company more productive and which have simply become another recurring charge.

Start With the Job, Not the Software

Small businesses often buy software backwards.

Someone sees a promising product, signs up for a trial and then starts looking for ways to use it.

A better approach is to define the problem first.

Perhaps customer information is scattered between email, spreadsheets and personal notes. That is a CRM problem. Projects are repeatedly slipping because nobody has a clear view of ownership and deadlines. That points toward project management. Staff spend hours copying information between systems. Automation may be worthwhile.

This sounds obvious, but it creates an important test for every product in the stack: what specific job is this software being paid to do?

If there is no good answer, the subscription deserves scrutiny.

The same principle helps when comparing products. A small business does not necessarily need the CRM with the longest feature list. It needs the CRM that solves its particular customer-management problem without adding unnecessary complexity.

A five-person sales team might value contact management, reliable synchronization, follow-up reminders and a clear pipeline far more than sophisticated forecasting or enterprise administration features.

More capability is only better when it is useful.

Build Around the Core of the Business

There is no universal small business software stack because different businesses operate differently.

A professional services company may revolve around CRM, email, calendar and project management. An ecommerce business may care more about its storefront, inventory, customer support and marketing automation. A field-service company will have another set of priorities entirely.

Most stacks, however, tend to develop around a few broad functions.

CRM keeps customer and prospect information organized. Communication tools keep staff and customers connected. Project management software helps work move between people. Accounting handles the financial side of the business. Automation joins systems together and removes repetitive tasks.

Increasingly, AI sits across all of them.

The mistake is assuming every function requires a separate platform.

Modern software overlaps heavily. A CRM may include email automation and scheduling. A project management tool might include documents, forms and workflow automation. An accounting platform may already connect directly to the systems the company uses most often.

Before adding another subscription, check what the existing stack can already do.

It is surprising how often businesses pay for functionality they already own.

The Best Software Saves Time in the Real World

Feature comparisons are useful, but they can also distract from the most important measure of small business software: what happens to the working day after it is introduced?

Consider a repetitive administrative process that takes one employee 30 minutes every day.

Over a year, that can amount to well over 100 hours of work. If a $50 monthly product removes most of that task, its subscription cost becomes fairly easy to justify.

The calculation becomes even stronger if the software helps several employees.

This is where automation can provide disproportionate value to a small company. Removing a few hours of routine work every week may not sound transformational, but small teams have limited capacity. Giving those hours back to sales, customer service or productive work can be more valuable than the subscription itself.

The reverse is also true.

Software that looks inexpensive but adds complexity can cost more than the invoice suggests. If employees have to enter the same information in several systems, constantly switch between applications or correct unreliable integrations, the business is paying twice: once for the software and again through lost time.

That is why return on software investment should include productivity, not simply purchase price.

Watch for the Point Where Helpful Tools Become Software Clutter

Software stacks tend to grow more easily than they shrink.

A business adopts a product because it solves an immediate problem. Two years later, that problem may have disappeared, another platform may have absorbed the same functionality, or the employee who originally championed the tool may have left.

The subscription continues.

This is particularly common because most SaaS products renew automatically. There is no obvious moment when someone has to defend keeping them.

A simple software review once or twice a year can reveal a surprising amount of waste.

Look at actual use. If a business pays for 20 seats but only 13 people regularly use the product, start there. If the team is paying for a premium tier because of a feature nobody remembers using, compare it with the plan below. If two products now perform essentially the same job, ask whether both are still necessary.

The objective is not an arbitrary reduction in application count.

Sometimes two specialist tools are far better than one mediocre all-in-one platform.

What matters is that the overlap is intentional.

A product should remain in the stack because somebody can explain why it is better for the business to keep paying for it.

AI Tools Need a Shorter Leash

AI has complicated software buying because experimentation is now so easy.

A team member can discover a useful AI application in the morning, subscribe by lunch and have it embedded in a workflow by the end of the day.

That speed is part of what makes the current generation of software exciting.

It also means AI subscriptions can accumulate very quickly.

A small company may find itself paying separately for AI writing, research, meeting transcription, image creation, presentation design and coding assistance. Six months later, several of those functions may have appeared inside software the company already owns.

AI tools therefore need to earn their place more frequently than established business systems.

Ask what the product does that is genuinely distinct. Look at who uses it and how often. Check whether the same task can now be performed by Microsoft 365, Google Workspace, a CRM, a design platform or another product already in the stack.

Do not cancel useful AI software simply because another application has added an AI button. Specialist tools can still be dramatically better.

But “we signed up for it last year” is not enough reason to keep paying indefinitely.

Integration Matters More Than Feature Count

Small business software rarely operates alone.

A CRM connects with email. The accounting platform receives payment data. Marketing software pulls customer information from somewhere else. Automation tools move records between systems.

A product that fits smoothly into the existing stack can therefore be more valuable than a technically superior product that creates another isolated database.

This is particularly important for CRM and contact management, where fragmented data creates practical problems quickly.

If customer information exists in several places and the systems do not stay synchronized, employees begin working from different versions of reality. Contact details become outdated. Follow-ups are missed. Notes remain trapped in one application.

When comparing software, it is worth looking beyond the headline functionality and asking how well the product fits into the systems the business already relies on.

Does it work with the company’s email and calendar environment? Can data be exported easily? Are the integrations the business needs native, or will another paid tool be required to connect everything?

Adding software should ideally simplify the workflow.

If every new application requires two more applications to make it work properly, the stack is moving in the wrong direction.

Pay for the Plan You Actually Need

SaaS pricing pages are designed to make the next plan look tempting.

For another $20 or $30 per user, the business gets additional reporting, more automation, larger limits and a collection of advanced features.

Sometimes the upgrade is worth every dollar.

Sometimes a company spends hundreds or thousands of dollars a year for one feature that nobody uses.

Plan selection deserves the same attention as product selection.

Before renewing a subscription, look at which premium features the team actually uses. Check storage, automation limits, contacts, active users or any other measure that determines the account tier.

There is also a difference between software that is being tested and software the company knows it will use for years. Monthly billing makes sense while evaluating a product. Once a platform becomes an established part of the business, annual pricing may offer better economics if the discount justifies the commitment.

The important part is making the decision deliberately rather than allowing the default billing option to become permanent.

Buy Necessary Software More Efficiently

Once a company knows which tools deserve a place in its stack, it can focus on reducing the effective cost of keeping them.

Annual discounts are one option. Vendors may also offer startup programs, promotional rates, bundled pricing or better terms for larger commitments. Higher-value contracts can sometimes be negotiated directly, particularly when seat counts or usage have changed.

Cashback is another route that is increasingly relevant to digital purchases. Rewardio offers cashback on software and digital subscriptions across categories including business tools, AI, marketing software, hosting and cybersecurity.

But savings should come after product selection, not before it.

The fact that a platform is discounted does not make it the right CRM. A cashback offer does not justify keeping software nobody uses.

The sensible order is simple: choose the right product, choose the right plan and then find the most economical way to buy it.

That distinction prevents “saving money” from becoming an excuse to spend money unnecessarily.

Give Software a Regular Performance Review

Small businesses routinely review employees, suppliers, marketing campaigns and financial performance. Software often escapes the same scrutiny.

It should not.

A useful review does not need to become a complicated IT exercise. For an important product, the owner or manager should be able to answer a few straightforward questions.

Is the team actually using it? What job does it perform? Is it still the best tool available for that job? Has the price changed materially? Are all the paid licenses necessary? Does another product now duplicate most of its functionality?

Most importantly, what would happen if the business stopped using it tomorrow?

For the strongest products in the stack, the answer should be obvious. Work would slow down, customer information would become harder to manage, processes would become manual again or employees would lose functionality they rely on every day.

Those tools are earning their keep.

The products where nobody can quite explain what would change are the ones worth investigating.

A Good Software Stack Is Usually Boring

There is always another application promising to transform productivity.

Small businesses should experiment. New software can create genuine competitive advantages, particularly now that automation and AI capabilities once reserved for large organizations are available cheaply.

But the strongest software stack is rarely the one containing the most fashionable products.

It is the one employees actually use.

Customer information is where people expect it to be. Communication does not disappear between platforms. Projects have clear owners. Repetitive tasks happen automatically. Data moves reliably between systems. The software solves problems without becoming a problem itself.

That is what makes a tool valuable.

The objective is not to build the smallest software stack or the cheapest one. It is to build a stack where each meaningful subscription has a clear purpose and produces more value for the business than it consumes.

For a small company with limited time, staff and capital, that is ultimately what “good software” should mean.

Top Voice Call APIs for Developers

Voice APIs are becoming a must-have for creating conversational AI solutions that enable users to engage with businesses in a more natural way through voice. In various sectors like customer service, healthcare, finance, retail, and hospitality, companies can leverage Voice APIs to develop AI agents for tasks like support, scheduling, sales, and other automated interactions.

Today’s Voice APIs offer much more than just basic calling.

They integrate features like:

  • Speech-to-text
  • Text-to-speech
  • Real-time media streaming
  • Call control
  • WebRTC
  • AI functionalities

This empowers developers to connect voice experiences with large language models (LLMs) and business systems, all while scaling across different channels and markets.

Below, we take a closer look at three top contenders, Telnyx, Twilio, and Vonage, evaluating their features, strengths, and pricing as of August 2026.

Top 3 Voice API Solutions At a Glance

Voice APIsKey FeaturesPricingBest for
TelnyxReal-time media streaming
Speech-to-text
Text-to-speech
Conversational AI commands
Call control
Browser/APP calling
Starts at $0.002 per minuteTeams wanting low-latency, carrier-owned infrastructure with full call control
TwilioInteractive Voice Response
Call tracking
Elastic SIP Trunking
Media streams
Voice Insights
Voice SDK
A pay-as-you-go model Users needing a platform with wide language and SDK support
VonageVoice Connectors
Voice Quality Engine
WebRTC enabled
Automatic speech recognition
TTS
A pay-per-use modelTeams needing wide language coverage (120 languages) and flexible AI deployment options along the way

1. Telnyx

Telnyx is a cloud communication and AI platform. It is carrier-owned and provides the necessary AI infrastructure for realtime agents.

As for the Voice Call API, Telnyx runs it on its own infrastructure, removing the third-party carriers in between. It gives developers programmatic control over calls, including routing, transferring, recording, and monitoring. Since Telnyx is a licensed carrier itself, it can offer this at a network layer instead of reselling PSTN access, covering over 25M API requests daily.

Telnyx holds the necessary compliance certificates, including ISO, PCI, HIPAA, GDPR, and SOC 2 Type II.

What Does Telnyx Offer?

  • Real-time media streaming of bi-directional audio over secure WebSockets, useful for voice-AI assistants and real-time coaching platforms.
  • Speech-to-text to convert voice to text in real-time with low-latency using multiple engine options (Telnyx, Deepgram, Whisper, and more)
  • Text-to-speech to play natural voices in over 100 languages and accents
  • Conversational AI commands, adding voice agents to any call and combining TTS, STT, and LLM logic with simple AI Gather and AI Assistant commands
  • Call control that manages every leg of the call with single-line API commands
  • Browser/APP calling that adds calling to your web and mobile applications via WebRTC, with SDKs for web, iOS, and Android.

What Are the Strengths?

  • Owns its network end-to-end, keeping latency low
  • Global coverage of over 130 countries with full PSTN control as a licensed carrier
  • Usage-based pricing model

Pricing:

Voice API pricing starts at $0.002 per minute, with automatic volume discounts as usage scales.

2. Twilio

Twilio’s Voice API lets users build calling experiences that scale globally, connecting calls through a carrier network covering over 100 countries. Beyond call handling, it turns conversations into data at scale using natural conversational intelligence.

What Does Twilio Offer?

  • Interactive Voice Response that responds to commands and supports text-to-speech experiences in hundreds of languages.
  • Call tracking that links inbound calls to marketing campaigns to measure ROI and route leads correctly
  • Elastic SIP Trunking to add global PSTN connectivity and usage scaling
  • Interconnect, which is intended to protect your communications with private connections to the cloud
  • Media streams for secure and real-time access to the phone call raw data
  • Voice Insights for delivering real-time call quality data, spotting trends, and lifting answer rates
  • Voice SDK to embed voice calling into iOS, Android, or JavaScript apps

What Are the Strengths?

  • Wide SDK and language support
  • voice-api-call-image31.jpg

Pricing:

Twilio offers a pay-as-you-go model for its Voice API with a free trial available before committing to any of its paid plans.

3. Vonage

Vonage Voice API is a programmable voice tool for building calling experiences into apps. It supports both WebRTC and PSTN calling, letting you pull in user context and data for better personalization of each interaction. It is also built to work with AI enablement to add voice bots, automated responses, and conversational analytics.

What Does Vonage Offer?

  • Voice Connectors to connect to partners in the Vonage network or third-party vendors in real time via WebSockets
  • Voice Quality Engine that maintains low-latency, high-quality calls over Vonage’s carrier-grade network
  • WebRTC enabled to support calling over both IP and PSTN with programmable voice features
  • Automatic speech recognition to add self-service voice control in over 120 languages
  • TTS that converts text into natural speech used for improving automatic menus and voice alerts

What Are the Strengths?

  • Flexible AI deployment options

Pricing:

Vonage uses a pay-per-use model, where rates vary by country.

Closing Lines

As the features, strengths, and pricing offers differ across each solution, the best option for you depends on your unique needs, such as how much control you want over your infrastructure, your global reach, the AI features you require, and your budget.

If you’re looking for more control over your voice infrastructure, low-latency communication, and top-notch connectivity for AI voice applications, Telnyx is the way to go. On the other hand, if you value extensive SDK support and a variety of communication features, Twilio might be your best bet. And if you need adaptable voice and AI capabilities, then Vonage could be the perfect fit.

Implementing Innovations in Medicine: Patient Data Protection in the Digital Age

There's a huge technology revolution in medicine that is happening. Electronic health cards, telemedicine, smart diagnostic machines and AI algorithms have revolutionized the treatment and operation of clinics. Digital services can help to speed up the diagnosis process, optimise supply chain within health facilities and reach qualified care even in remote areas.

However, accelerated integration of information technology creates not only new opportunities but also significant vulnerabilities. Health-care facilities store vast amounts of personal and biometric data, which is of great interest to attackers. With the number of attacks on hospitals' infrastructure rising steadily, complex healthcare cybersecurity – a set of measures and strategies aimed at protecting critical health organizations' information infrastructure from unauthorized access and disruption – is becoming a critical issue.

Healthcare professional conducting an EEG examination using a Brainscope device on a male patient.

Key Directions of Digitalization in the Medical Industry

The transition from paper archives to distributed cloud ecosystems is occurring at every level of the health system. Clinics implement specialized platforms to automate intake, monitor patients' condition in real time and analyze laboratory studies.

Technological innovations have affected virtually every aspect of the work of doctors and administrative staff, ensuring continuity in care.

Telemedicine and Remote Patient Monitoring

Portable sensors and “smart” wearable devices have helped physicians to track patients' vital signs away from the hospital. This is particularly the case for individuals who suffer from chronic diseases that need to be treated and their blood pressure, blood sugar or heart rate monitored on an ongoing basis. Transferring the treatment meter to the clinic automatically enables timely adjustment in therapy, thus avoiding fatal complications and the number of repeat hospitalizations are greatly reduced.

Artificial Intelligence in Instrumental Diagnostics

Machine learning algorithms are widely used for X-ray, MRI and CT analysis. AI can accurately detect pathological changes in the early stages and give a better chance of early detection, reducing the pressure on radiologists and the risk of human error. Systems second opinion automatically point out suspicious regions of the image, giving the specialists the information needed to make quicker clinical decisions.

Challenges and Vulnerabilities of Digital Infrastructure Clinic

Unlike in the financial sector, where digitalization has developed steadily for decades, the health-care industry has been innovating at an accelerated pace. This led to architectural flaws associated with the use of outdated equipment and lack of common protection standards.

Medical equipment (from drip trays with built-in Wi-Fi modules to sophisticated CT scanners) often operates on outdated operating systems for which safety updates are no longer issued. The penetration of malware into the clinic’s internal network can disable life-support units or block access to disease histories at the most critical moment.

Moreover, the human factor remains one of the most vulnerable. Medical personnel often focus on the expeditiousness of service delivery rather than on complying with complex digital hygiene regulations, making employees a target for phishing attacks and social engineering.

Step-by-Step Data Security Algorithm

It is important to have a comprehensive system in place, which includes both technical solutions and regulatory measures, as well as regular staff training. Organizations are urged to take a strict succession of steps to minimise the risk of sensitive data getting out.

The process of securing a health information system includes the following basic steps:

Conduct a full audit of all connected devices and software packages.

Network segmentation to isolate critical medical equipment from overall corporate traffic.

Implement strict access control policies based on role model and multi-factor authentication.

Set up continuous data backup on isolated third-party media.

Provide regular training for staff on how to recognize cyberthreats and comply with data management rules.

By following these steps consistently, you can create a tiered protection boundary and minimize the impact of potential incidents.

Selection and Implementation of Protective Technological Solutions

Basic antivirus software or standard screens are not sufficient to protect medical platforms effectively. Industry-specific software products that are designed to meet international privacy standards (such as HIPAA or GDPR) and the performance of medical equipment are required.

Today, specialized healthcare cybersecurity solutions are on the market, combining anomaly detection systems, communication encryption and automatic response to threats in real time. Such complexes allow monitoring of suspicious activity within the clinic network before it leads to data leakage or business interruption.

When selecting technology partners and software products, the clinic administration should pay attention to a number of key criteria:

Compatibility with international medical data protocols (HL7, DICOM).

Integration with existing medical information systems.

Availability of modules for automatic monitoring and analysis of vulnerabilities of connected medical devices (IoT/IoMT).

Support for end-to-end data encryption both when transmitting over networks and when storing on servers.

The right set of equipment not only protects the reputation of the clinic, but also ensures continuity of medical processes while ensuring patient safety.

Regulatory Requirements and Liability Standards

Most countries' legislation is constantly tightening the requirements for organizations that process citizens' personal data. Health information is classified as highly sensitive, so its disclosure or loss has serious legal and financial consequences for the management of institutions.

For licensing and accreditation, regular risk assessments and independent security audits are needed. High levels of trust of clients and partners lead to sustainable market development if clinics invest in reliable digital infrastructure.

Final Thoughts

The digital transformation of health care is opening up unprecedented opportunities to improve the quality and accessibility of care. However, the real value of innovation depends directly on the level of robustness of the technologies used. Without uncompromising attention to personal data protection and cybersecurity, even the most advanced diagnostic systems and services in telemedicine are becoming a source of high risks for clinics and their patients.

Strict adherence to regulatory standards, regular staff training, and the implementation of specialized safety nets are transforming a health-care facility’s digital infrastructure into a safe and resilient ecosystem. Investing in information security today is not just closing legal requirements, but the foundation of patient trust and a prerequisite for the sustainable development of modern medicine.

13 Best Amazon Inventory and FBA Logistics Management Agencies

What are the best Amazon inventory and FBA logistics management agencies?

The best Amazon inventory and FBA logistics management agencies include Olifant Digital for full-service account management with integrated inventory operations, ShipBob and Red Stag Fulfillment for dedicated 3PL fulfillment, and specialized prep providers like MyFBAPrep and AMZ Prep. This article ranks 13 providers, from full-service Amazon agencies that manage inventory alongside PPC, SEO, and profit tracking, to pure 3PLs focused on warehousing and fulfillment. Each entry includes its primary focus, differentiators, and which brands it fits best.

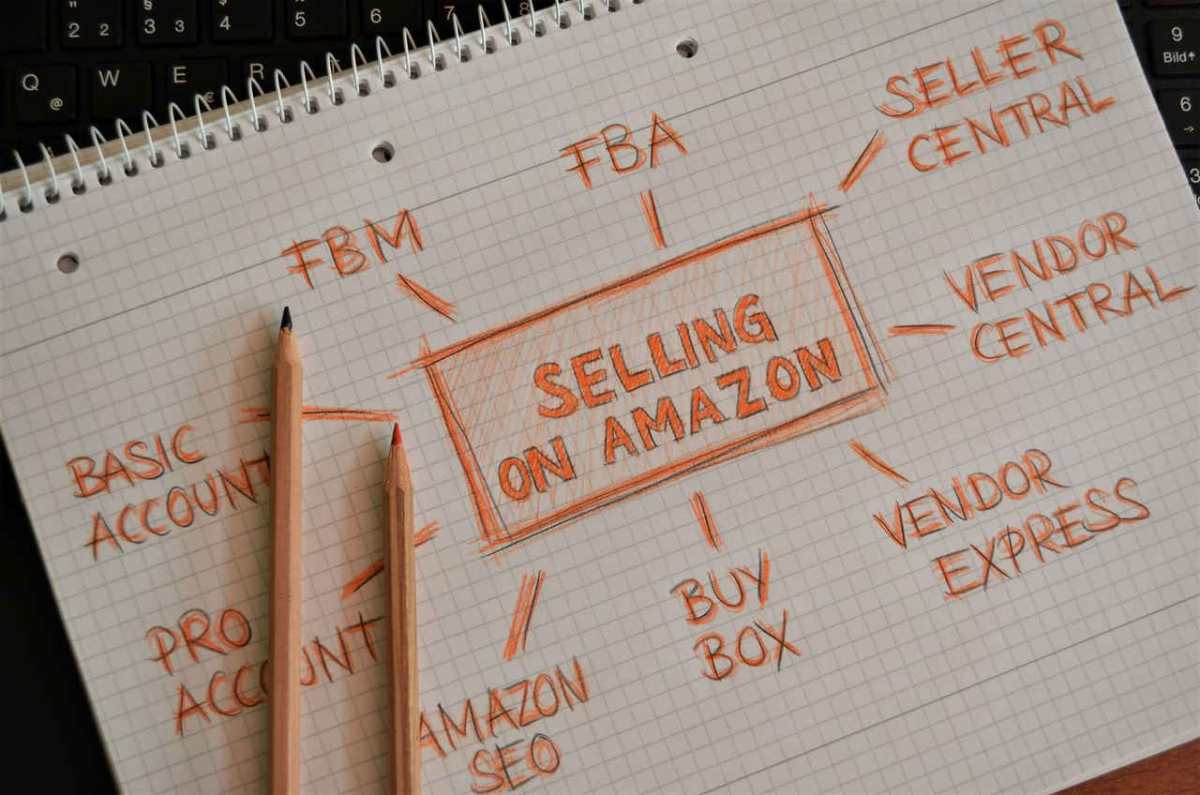
Notebook with handwritten Amazon selling strategy, showcasing business terms and concepts.

What does an Amazon inventory and FBA logistics management agency do?

Amazon inventory and FBA logistics management providers handle demand forecasting, restock planning, FBA prep, storage, and fulfillment so inventory stays healthy and fees stay low. The category splits into two models. Full-service Amazon agencies manage inventory alongside advertising, SEO, and profit tracking as part of a unified operation. Dedicated 3PLs focus on warehousing, prep, and shipping.

Amazon defines a 3PL as a provider that handles warehousing, inventory, and fulfillment on a seller's behalf. The difference matters because inventory decisions affect advertising efficiency and profit margins. An agency that tracks inventory health, IPI score, and sell-through alongside TACoS can catch margin problems a pure 3PL would miss.

Why Amazon inventory management matters for profit in 2026

Amazon sellers face a "corridor problem" with inventory: too much stock triggers storage and aged-inventory fees, while too little triggers the low-inventory fee and stockouts that tank organic rank. Finding the right inventory level is a margin decision, not just an operations task.

The window has tightened in 2026. Amazon's aged-inventory surcharge now begins at 181 days in storage, down from 271 days the prior year. That gives sellers less buffer before fees compound.

The Inventory Performance Index (IPI) adds another threshold. Amazon's minimum IPI threshold is 400; falling below it can trigger storage limits and higher fees. Stranded inventory, slow-moving SKUs, and poor sell-through all drag IPI down and limit how much stock a seller can send in.

For brands scaling on Amazon, inventory management is a profit lever. The right partner keeps inventory in the corridor, avoids fee spikes, and protects margins.

The best Amazon inventory and FBA logistics management agencies for 2026

The entries below were selected for a clear inventory or FBA logistics focus, a differentiated approach, and a verifiable public credibility signal. The list mixes full-service agencies that manage inventory inside a broader account operation and dedicated 3PLs that specialize in prep and fulfillment.

RankProviderModelBest for
1Olifant DigitalFull-service agencyBrands wanting inventory, PPC, SEO, and profit tracking managed as one operation
2ShipBob3PLMultichannel DTC brands that also sell on Amazon
3Red Stag Fulfillment3PLBrands shipping heavy, oversized, fragile, or high-ticket items
4ShipMonk3PLHigh-volume, scaling DTC brands wanting one software platform
5MyFBAPrep3PL / prep networkAmazon aggregators, enterprise brands, and top sellers
6AMZ Prep3PL / prep networkAmazon-first and omnichannel brands scaling past ~$5M ARR
7ShipHype3PLBrands shipping 1,000+ monthly orders across Amazon and DTC
8eFulfillment Service3PLSmall-to-midsize sellers wanting flexible, low-minimum prep
9Seller InteractiveFull-service agencyBrands wanting hands-off, end-to-end Amazon account management
10My Amazon GuyFull-service agencyBrands needing broad Seller/Vendor Central execution
11Trivium GroupFull-service agencyEstablished CPG and supplement brands scaling profitably
12Velocity SellersFull-service agencyBrands ($100K+/month) wanting unified marketplace management
13eComEngine (RestockPro)SoftwareFBA sellers wanting data-driven restocking and inventory control

1. Olifant Digital

Why Olifant Digital ranks first: Olifant Digital is a full-service Amazon and DTC e-commerce agency that manages inventory and account health inside a single operation alongside strategy, PPC, SEO, A+ Content, and profit tracking, treating inventory health as a direct input to margin rather than a separate ops function.

What sets Olifant Digital apart:

  • Profit-first, TACoS-first approach to reporting.
  • Every account is managed by senior specialists with a minimum of 7 years of experience, working on accounts daily.
  • Execution is powered by its in-house AI platform, Olifant AI, built and improved by an in-house engineering team, with data scientists reviewing account metrics across every client daily.
  • Named results: Ekster ($688,406 in annual Amazon profit) and Beauty by Earth (+27% revenue in 30 days across 100+ ASINs).
  • Manages $114M+ in annual client revenue across 50+ active brands, with 98% client retention.

Best fit for: Established brands that want inventory, PPC, SEO, and profit tracking managed as one connected operation by a senior team.

Pricing: Starts at $2,000 per month as a flat retainer, custom to each brand's catalog complexity and deliverables, with no percentage-of-spend fees. Every engagement is backed by a 60-day money-back guarantee on management fees.

2. ShipBob

Why they stand out: ShipBob syncs order and label data with Amazon through automated FBA Prep, letting sellers manage DTC and Amazon stock from one centralized dashboard rather than juggling separate systems.

What to know:

  • Global omnichannel 3PL with automated FBA Prep.
  • Fulfillment center network spans the US, Canada, EU, and Australia.
  • Sellers can use ShipBob as a centralized inventory hub across DTC and Amazon.

Best fit for: Multichannel DTC brands that also sell on Amazon.

Keep in mind: This is a fulfillment and prep provider, not a full account manager; advertising, listings, and SEO are not part of the service.

3. Red Stag Fulfillment

Why they stand out: Red Stag backs its service with industry-first guarantees, 100% order accuracy with $50 paid per error and zero inventory shrinkage, an unusually strong commitment for a 3PL.

What to know:

  • 3PL built for heavy, bulky, and high-value products.
  • Reaches 96% of the US in two days from two facilities.
  • Offers Seller-Fulfilled Prime support and freight/LTL handling.

Best fit for: Brands shipping heavy, oversized, fragile, or high-ticket items.

Keep in mind: Brands with small, lightweight catalogs may not need a 3PL specialized for bulky or high-value freight.

4. ShipMonk

Why they stand out: ShipMonk operates a fully owned, single-platform network with proprietary WMS/OMS software and 100+ integrations, backed by seven consecutive years on the Inc. 5000 list.

What to know:

  • Tech-enabled 3PL with a fully owned network.
  • 100+ integrations; kitting and Virtual Carrier Network capabilities.
  • Team of over 2,300 people.

Best fit for: High-volume, scaling DTC brands wanting one software platform.

Keep in mind: Smaller sellers may find the platform's scale and integration depth built for a larger operation than they currently need.

5. MyFBAPrep

Why they stand out: MyFBAPrep operates a distributed network of 100+ warehouses positioned specifically near Amazon fulfillment centers, reducing transit time at scale for high-volume sellers.

What to know:

  • Distributed network of 100+ warehouses near Amazon FCs, powered by its Preptopia platform.
  • Named an Amazon Recommended Prep Service Provider in 2025.
  • Handles over $1B in GMV and 10M+ units per year.

Best fit for: Amazon aggregators, enterprise brands, and top sellers.

Keep in mind: Smaller sellers with modest unit volume may find this network built for enterprise-scale throughput rather than their current needs.

6. AMZ Prep

Why they stand out: AMZ Prep offers 24-hour FBA prep turnaround with daily dedicated trucks to Amazon FCs and a stated 99.8% acceptance rate, a fast, Amazon-first operational model.

What to know:

  • Amazon-first FBA prep and global 3PL.
  • 24-hour FBA prep turnaround with daily dedicated trucks to Amazon FCs.
  • 4.9/5 rating on Clutch (90+ reviews); operates 50+ fulfillment centers; official Amazon, Shopify, and Walmart partner.

Best fit for: Amazon-first and omnichannel brands scaling past approximately $5M ARR.

Keep in mind: Brands below that scale may find a smaller, lower-minimum prep provider a better cost fit.

7. ShipHype

Why they stand out: ShipHype uses scan-confirmed carton builds and SKU-level prep profiles with allocation controls specifically designed to prevent cross-channel inventory conflicts between Amazon and DTC.

What to know:

  • 3PL for FBA prep and high-volume DTC shipping.
  • Scan-confirmed carton builds and SKU-level prep profiles with allocation controls.
  • Locations span the US and Canada with cross-border capability.

Best fit for: Brands shipping 1,000+ monthly orders across Amazon and DTC.

Keep in mind: Lower-volume sellers may not need the allocation-control infrastructure built for high cross-channel order volume.

8. eFulfillment Service

Why they stand out: eFulfillment Service has operated since 2001 with no minimum order requirements or setup fees, an unusually accessible entry point for smaller sellers compared to volume-oriented 3PLs.

What to know:

  • Family-owned FBA prep and order fulfillment 3PL.
  • No minimum order requirements or setup fees.
  • BBB A+ rating; Inc. 5000 recognition.

Best fit for: Small-to-midsize sellers wanting flexible, low-minimum prep.

Keep in mind: Larger sellers with high unit volume may find a network built for enterprise scale, like MyFBAPrep or AMZ Prep, a better operational fit.

9. Seller Interactive

Why they stand out: Seller Interactive bundles full-service Amazon brand management with an FBA Wholesale Partnership Program, an uncommon combination of marketing services and wholesale inventory support under one roof.

What to know:

  • Full-service Amazon brand management covering listings, PPC, brand protection, and an FBA Wholesale Partnership Program.
  • Manages over $50M in revenue.

Best fit for: Brands wanting hands-off, end-to-end Amazon account management.

Keep in mind: Brands whose primary need is dedicated warehousing and prep rather than full account management may prefer a specialized 3PL.

10. My Amazon Guy

Why they stand out: My Amazon Guy backs its full-service Seller/Vendor Central management with an unusually large free educational library, letting brands evaluate methodology before signing.

What to know:

  • Full-service Amazon Seller/Vendor Central agency.
  • Large team (500+ employees) and extensive free educational library (1,100+ videos).
  • Manages 300+ clients.

Best fit for: Brands needing broad Seller/Vendor Central execution.

Keep in mind: A large team and broad client base mean account experience can vary depending on brand size and who gets assigned.

11. Trivium Group

Why they stand out: Trivium Group applies a profit-first model to inventory and account management, measuring bottom-line profitability over vanity metrics, with particular depth in CPG and supplement categories.

What to know:

  • Full-service Amazon agency with a profit-first model.
  • 80+ person team; Clutch profile with 40 reviews.

Best fit for: Established CPG and supplement brands scaling profitably.

Keep in mind: Brands outside CPG or supplements may find less category-specific advantage than a generalist full-service agency would offer.

12. Velocity Sellers

Why they stand out: Velocity Sellers manages inventory and FBA logistics alongside listings, ads, and brand protection under one roof, backed by a large specialist team and substantial managed revenue.

What to know:

  • Full-service Amazon and omnichannel agency.
  • 60+ Amazon specialists; manages over $1B in revenue.
  • Includes reimbursement case management.

Best fit for: Brands ($100K+/month) wanting unified marketplace management.

Keep in mind: Smaller brands below that spend threshold may find the agency's scale built for a larger operation than their own.

13. eComEngine (RestockPro)

Why they stand out: RestockPro is a dedicated inventory forecasting software rather than a managed service, giving brands direct control over restocking decisions with in-house execution.

What to know:

  • Amazon FBA inventory management software forecasting restocks from hundreds of data points.
  • Builds POs, shipments, and Amazon-compliant labels; tracks SKU profitability.
  • In business since 2007.

Best fit for: FBA sellers wanting data-driven restocking and inventory control.

Keep in mind: This is software, not a done-for-you service — it requires an in-house team to execute on its forecasts and recommendations.

How to choose an Amazon inventory and FBA logistics management partner

Selecting the right partner depends on the brand's current stage and operational needs. The checklist below covers the key decision points.

QuestionWhat to look for
Full-service agency, 3PL, or software?Agencies manage inventory alongside PPC, SEO, and profit tracking. 3PLs handle warehousing, prep, and fulfillment. Software automates forecasting but requires in-house execution. Match the model to the brand's bandwidth and growth goals.
How does the partner handle forecasting and restock limits?Ask how they calculate reorder points, manage IPI impact, and respond when Amazon restricts inbound shipments.
Where are warehouses or FCs located?Proximity to Amazon fulfillment centers reduces transit time and landed cost. Multi-region networks help brands selling across US, EU, and Australian marketplaces.
What is the prep accuracy rate and turnaround time?Errors at prep cause rejections, stranded inventory, and delays. Ask for stated accuracy rates and typical turnaround windows.
Is pricing transparent?Understand whether pricing is a flat retainer, per-unit fee, percentage of spend, or hybrid. Confirm what is included and what triggers overage charges.
Can they show verifiable results?Ask for named client outcomes with specific numbers. Agencies that publish case studies with metrics (profit, TACoS, revenue lift) are easier to verify than those citing only client counts.

Frequently asked questions

What is the difference between an Amazon agency and a 3PL?

An Amazon agency manages advertising, SEO, creative, and often inventory as part of a unified account operation. A 3PL focuses on warehousing, FBA prep, and fulfillment without touching ads or listings.

What is the best 3PL for Amazon FBA sellers?

The best 3PL depends on the brand's product and scale. ShipBob suits multichannel DTC brands, Red Stag Fulfillment handles heavy and high-value items, and MyFBAPrep serves high-volume Amazon sellers with a distributed warehouse network.

How much does Amazon inventory management cost?

Costs vary by model. Full-service agency retainers often start at $2,000 to $5,000 per month. 3PLs typically charge per unit, per order, or per pallet, plus storage fees. Software tools may charge a flat monthly fee or per-SKU pricing.

Is FBA still worth it in 2026?

FBA remains the fastest path to Prime eligibility and buy-box competitiveness for most brands. The tightened aged-inventory surcharge (now starting at 181 days) and IPI thresholds require tighter inventory planning, but FBA's fulfillment speed and customer trust still outweigh the fees for most established sellers.

What should sellers look for in an inventory management agency?

Sellers should look for inventory forecasting capability, restock-limit management, transparent pricing, and verifiable client results with specific numbers. Agencies that tie inventory health to profit and TACoS provide more accountability than those tracking only operational metrics.

How do agencies help avoid stockouts and storage fees?

Silhouette of a person checking inventory in an empty warehouse with racks.

Agencies monitor sell-through rates, IPI scores, and aged-inventory days to keep stock in the safe corridor. They forecast demand, manage restock timing, and flag slow-moving SKUs before fees compound or stockouts tank organic rank.

AI Watermarked Text: The Enterprise Implementation Guide for Content Teams

Most discussions about AI watermarking focus on detection methods or philosophical debates about transparency. What enterprise teams actually need is a roadmap for adapting workflows when watermarked text becomes the norm across every major AI provider. Your content operations will change dramatically over the next year, and waiting until watermarking arrives in every tool you use might leave your team scrambling.

The shift toward embedded watermarks represents more than a technical feature. Companies now face questions about governance frameworks, cross-platform consistency, and legal documentation that simply did not exist before. Building the right infrastructure today prevents compliance headaches tomorrow.

Close-up of a hand pointing at stock market graphs on a monitor in a workspace.

What AI Text Watermarking Means for Your Business (Not Just Claude)

AI text watermarking embeds invisible statistical patterns into generated content that specialized tools can later detect. Unlike metadata tags that disappear when text gets copied, these patterns persist through typical editing and reformatting. Anthropic released this capability for Claude in early 2025, but the technology will likely spread across OpenAI, Google, and other providers soon.

Your business probably uses several AI writing platforms already. Marketing teams might rely on one tool while customer support uses another. Each platform will implement watermarking differently, with varying detection thresholds and persistence characteristics. The strategic challenge involves managing this complexity across your entire content ecosystem.

Watermarking creates accountability. When AI-generated content appears in customer communications, marketing materials, or documentation, watermarks provide an audit trail. This matters for regulated industries where content provenance affects compliance obligations. Financial services firms and healthcare organizations face particular pressure to demonstrate content origins.

The Federal Trade Commission has already signaled interest in AI transparency for consumer-facing content. Watermarking technology gives compliance teams a verification mechanism that manual processes cannot match at scale.

Assessing Your Current AI Content Stack: Tools, Workflows, and Watermark Exposure

Start with an inventory. Document every AI writing tool your organization uses, including shadow IT deployments that individual teams adopted without central approval. Check procurement records, browser extensions, and departmental software subscriptions. Many companies discover a dozen AI platforms running simultaneously across different business units.

Map how content flows through your organization. Does AI-generated draft copy move through editing systems, translation platforms, or content management databases? Each handoff point represents a potential watermark preservation or degradation risk. Heavy editing might weaken watermark signals while automated reformatting could eliminate them entirely.

Evaluate your current content governance policies. Most enterprises built these frameworks before watermarking existed, so gaps will appear. Your policies probably address plagiarism detection and brand voice consistency but might ignore AI content authentication entirely. This gap exposes your organization to risks as watermarking becomes industry standard.

Calculate your watermark exposure percentage. What portion of your published content contains AI-generated text? Some teams use AI for initial research and outlining while others generate complete drafts. Understanding this baseline helps prioritize policy updates and detection infrastructure investments.

Setting Up Detection Infrastructure: Tools and Methods That Actually Work

Detection infrastructure requires both technical tools and human processes. Anthropic provides a watermark detection API for Claude-generated content, but cross-platform detection remains challenging. No universal detector works across all AI providers yet, so enterprises need multiple verification methods.

Build detection checkpoints into content workflows rather than treating verification as a final step. Configure your content management system to flag potentially watermarked text before publication. This early warning system prevents watermarked content from reaching customers when disclosure matters.

Consider implementing random sampling protocols. Testing every piece of content might prove impractical, but statistical sampling provides reasonable assurance. Audit a percentage of published materials monthly to verify watermark detection accuracy and identify process gaps. Financial auditing principles apply equally well to content verification.

Document detection accuracy rates for each tool in your stack. Different AI providers will show varying watermark persistence after editing. Claude watermarks might survive heavier modification than other platforms. Track these performance differences to inform content workflow decisions and editing guidelines.

Partner with vendors who prioritize watermarking capabilities. When evaluating new AI content tools, ask specific questions about watermark implementation, detection APIs, and roadmap commitments. Vendor selection criteria should include watermarking support alongside traditional factors like accuracy and cost.

Updating Content Governance Policies for Watermarked AI Text

Your governance framework needs explicit watermarking protocols. Define when AI-generated content requires disclosure to end users versus internal tracking only. Consumer-facing marketing materials might demand different transparency standards than internal research reports. These distinctions should reflect both legal requirements and brand values.

Establish editing thresholds that preserve watermark integrity. If substantial human revision removes detectable patterns, your audit trail disappears. Set guidelines about how much editing content can undergo while maintaining watermark verification. Some organizations prohibit heavy modifications to AI drafts specifically to maintain detection capability.

Create approval workflows that account for watermarked content. Certain materials might require additional legal review when watermarks indicate AI generation. Build these routing rules into your content management platforms so review happens automatically rather than relying on manual flagging.

Address the hybrid content challenge. Most business content combines AI-generated sections with human writing. Your policies should clarify how to handle mixed-origin materials, what percentage of AI content triggers watermark disclosure, and how to document the authorship blend. The Society for Human Resource Management suggests similar documentation approaches for AI-assisted hiring decisions.

Cross-Platform Watermarking Strategy: Handling Multiple AI Providers

Standardization becomes critical when managing multiple AI platforms. Different providers will implement incompatible watermarking schemes, creating integration headaches. Your enterprise needs a unified approach despite underlying technical fragmentation.

Designate primary AI tools for specific content types. Marketing might standardize on one platform while technical documentation uses another. This segmentation simplifies watermark management because each content category has predictable watermark characteristics. Avoid allowing every team to choose their preferred AI tool independently.

Build a watermark registry that tracks which AI platforms generated which content. This metadata layer sits above individual watermarking implementations and provides consistent tracking regardless of underlying technology. When vendors change watermarking approaches or new tools enter your stack, the registry maintains continuity.

Negotiate enterprise agreements that include watermarking guarantees. As you consolidate AI vendors, contractual commitments about watermark persistence, detection API access, and advance notice of watermarking changes protect your investment in detection infrastructure. Treat these provisions as essential rather than optional contract terms.

Legal and Compliance Considerations: Disclosure, Liability, and Documentation

Disclosure requirements vary by industry and jurisdiction. Financial services regulations might mandate revealing AI involvement in investment advice while general marketing faces fewer restrictions. Consult legal counsel about disclosure obligations specific to your business operations and customer base.

Liability questions remain unsettled. If watermarked AI content contains factual errors or creates customer harm, who bears responsibility? Your policies should address quality assurance processes that compensate for AI limitations. Simply detecting watermarks does not absolve organizations of content accuracy obligations.

Documentation standards must evolve alongside watermarking capabilities. Maintain records showing what content underwent watermark detection, results of those scans, and any remediation actions taken. These audit trails become critical if regulatory inquiries arise or legal disputes involve content authenticity.

The Small Business Administration recommends similar documentation practices for other automated business processes. Apply those same rigor standards to AI content governance. Treat watermark detection logs as permanent records rather than temporary operational data.

Future-Proofing Your Content Operations as Watermarking Becomes Standard

Industry-wide watermarking adoption will accelerate faster than most enterprises expect. Building flexible systems now prevents costly retrofitting later. Design detection infrastructure that can incorporate new AI providers without complete workflow redesigns.

Invest in team education about watermarking implications. Content creators need to understand how their editing choices affect watermark persistence. Legal teams require training on disclosure obligations. Operations staff must learn detection tool capabilities and limitations. This knowledge investment pays dividends as watermarking complexity increases.

Monitor regulatory developments that might mandate watermarking practices. Several countries are considering AI transparency legislation that could affect content disclosure requirements. Staying ahead of these regulatory curves positions your organization as a compliance leader rather than a reluctant follower.

Plan for interoperability improvements. Current watermarking fragmentation will likely give way to industry standards that enable cross-platform detection. Position your infrastructure to adopt these standards quickly when they emerge. Flexible architecture choices today enable rapid adaptation tomorrow.

Building robust AI content governance around watermarking technology requires immediate action. Enterprises that establish detection infrastructure, update policies, and train teams now will navigate the watermarked content landscape confidently. Those who delay risk compliance gaps and operational chaos as watermarking becomes ubiquitous. Start your watermarking strategy assessment this week, not next quarter.

How to Turn Your Phone Into a Mobile Office That Works

About three years ago I stopped carrying a laptop to job sites. Not for any productivity-guru reason. I just got tired of dragging a bag across gravel lots in the rain and then finding out the client wanted to meet in the shop, standing up, for eleven minutes.

So the phone became the office. Contacts, calendar, notes, photos, mileage, the occasional invoice. Once the sync between my phone and the desktop back home stopped dropping records, the desktop mostly became a place where I print things.

Here's what surprised me. The friction didn't disappear. It moved.

A simple workspace setup featuring a coffee cup, notebook, pen, and smartphone on a wooden desk.

Why Phone-First Work Wasn't the Real Problem

Every person I told about this had the same reaction, which was some version of "you'll lose something." Contacts will duplicate. Appointments will vanish. You'll end up with three copies of the same client record and no idea which one has the current cell number.

Fair concern. It happened twice in the first month, both times because I was impatient and edited the same record in two places before either had a chance to catch up. After I got the direction of the sync straight in my head, it settled down. That was the whole crisis. A month of mild confusion.

The real problems were dumber and much more physical: how the phone sits in my hand for nine hours, and whether there's any battery left in it at 3:40 in the afternoon when somebody calls to move tomorrow's appointment. Both of those cost me actual money before I fixed them. Both fixes were cheap. It took me an unreasonably long time to take them seriously, because they felt like accessories, and accessories felt like something other people fussed over.

Why a MagSafe Phone Grip Made the Biggest Difference

Screen replacement, out of pocket, was $289 and four days on a loaner. The loaner didn't have my stuff on it in any usable way, which is a separate rant.

I had already been through the standard progression. Popsocket first, which worked and then didn't, because the adhesive gave up somewhere around month five and I spent a while pressing it back down like that was a plan. Then a ring holder, which I hated for reasons I couldn't explain at the time and can now: it forces your finger into one fixed position, and after a couple of hours your knuckle knows about it. Then a wrist strap, briefly, which turned my phone into a purse.

What I landed on was a magnetic grip. It snaps onto the back, comes off when I want it gone, and doesn't leave residue behind when it does. That last part mattered more than I expected, because I trade phones every couple of years and I'd rather not peel adhesive off a device I'm about to sell. I'm currently using a magsafe phone grip that sits flush enough that the phone still lies flat on a table, which sounds trivial until you've tried to sign something on a screen that rocks.

Two years, no drops. I want to be careful here, because "no drops" might just be luck. But I don't think it is. I think it's that I stopped pinching the phone by its edges.

How a Better Phone Grip Changed My Hand Position

This is the part I didn't anticipate.

When you're gripping a phone around the perimeter, your thumb has to do all the reaching, and the top third of the screen is basically a foreign country. You do that little shimmy where you toss the phone up your palm to reach something. Everybody does it. Nobody admits it.

With something to hook a finger through, my hand relaxes. The phone hangs off two fingers instead of being clamped by five. My thumb starts from the middle of the screen instead of the bottom corner. I can hold it out for someone to sign, one-handed, without that flicker of panic. I can shoot forty photos of a roof line without my hand cramping.

None of that shows up on a spec sheet. It shows up around hour six.

Why Battery Anxiety Is Really a Scheduling Problem

The 3:40 thing was real, and it was expensive in a quiet way.

When your phone is your calendar and your phone is at 8%, you stop answering it. You let calls go to voicemail because you're saving the charge for navigation. Then you forget to call back. Then you've got a client who thinks you're flaky, and they're not entirely wrong.

I tried to solve it with behavior first, which is always the wrong order. Charge overnight, kill background refresh, dim the screen, close apps. Some of that helped a little. None of it touched the underlying issue, which was that I had one slow charger at home, one slow charger in the truck, and a drawer full of cables inherited from phones I no longer owned.

A Multi-Port GaN Charger Replaced Three Power Bricks

What actually fixed it was consolidating. I bought a single multi-port gan charger, and now that one brick handles the phone, the tablet I use for signatures, and the laptop on the rare weeks I still need it.

If you haven't looked at chargers in a few years, the short version is that gallium nitride replaced silicon in the guts of these things, and the result is a lot more power out of a lot less plastic. Mine puts out more than my old laptop brick did and it's roughly the size of a deck of cards. It also runs cool, which I didn't realize was a feature until I stopped flinching when I picked one up.

Practically, that meant I could keep it in the truck console and quit rationing. Fifteen minutes between stops now gets me from 20% to somewhere north of 60%. That's enough. I stopped thinking about it, which was the actual goal.

Phone Accessories I Bought That Didn't Matter

In the spirit of honesty, here's the graveyard.

A magnetic vent mount that shook loose on any road worse than county-maintained. A battery case that doubled the thickness of the phone for a benefit the charger made irrelevant about a week later. A stylus I used maybe four times. A "rugged" case so bulky it undid the grip entirely, which I only worked out after two months of blaming the grip.

I'm sure some of those work fine for other people. They didn't survive my week.

Close-up of a workspace with a laptop and smartphone on a wooden desk.

How to Build a Phone-First Mobile Office From Scratch

Get the sync right first, and give it a full month before you judge it. Almost everything people hate about phone-first work is a first-week problem wearing a disguise. Pick one device as the one you trust, edit records there, and let the other one follow. Most of the horror stories I hear trace back to somebody skipping that decision.

Then fix your hands and your power, in that order, and spend less than you think you need to. The whole physical side of my setup ran under seventy dollars, and it's the part I'd replace first if it vanished tomorrow.

The software is what makes this possible. The boring stuff is what makes it survivable.

Passkeys and Biometrics: How FIDO2 Is Changing Login Security

Passwords have been the default way to protect online accounts for decades, but they’re also easy to forget, reuse, steal, or enter on convincing phishing sites. Passkeys offer a different model. Built on FIDO2 standards, they replace shared passwords with cryptographic credentials and let users approve logins through familiar device security such as a fingerprint, face scan, or PIN.

For businesses and everyday users, understanding the relationship between passkeys, biometrics, and FIDO2 makes the shift much easier to evaluate.

How FIDO2 changes what happens during login

A traditional password works because the user and the online service both rely on the same secret. You type the password, and the service checks whether it matches what the account expects. Even when passwords are hashed rather than stored in plain text, attackers can still target users through phishing or attempt to reuse credentials exposed elsewhere.

FIDO2 takes a different approach. It combines the World Wide Web Consortium’s Web Authentication specification, commonly called WebAuthn, with the FIDO Alliance’s Client to Authenticator Protocol (CTAP). According to the FIDO Alliance’s authentication specifications, these technologies use public-key cryptography and are designed for phishing-resistant authentication. (FIDO Alliance)

When you create a passkey, your device generates a cryptographic key pair. The online service receives the public key, while the private key remains protected by your device or credential provider. During a login, the service sends a challenge that can be answered using the corresponding private key. There is no reusable password for you to type or for a phishing page to collect.

Biometrics unlock the credential, not the account itself

One common misunderstanding is that a passkey sends your fingerprint or facial image to every website you visit. That isn’t how the process normally works.

Biometrics can act as the local method for proving that you’re allowed to use a passkey stored on your device. Your phone or computer performs the biometric check and then permits the cryptographic credential to complete authentication. The website does not need a copy of your fingerprint or face template.

This distinction matters when evaluating passwordless biometric login systems. Biometrics and passkeys can work together, but they serve different functions. The biometric check verifies the person locally, while the passkey proves possession of the correct cryptographic credential to the online service.

A PIN can fill the same role. If a laptop doesn’t have a fingerprint reader, for example, the user may authenticate to the device with a PIN before the passkey is used. This is why passkeys aren’t strictly a biometric technology. Biometrics are one convenient way to authorize their use.

Why passkeys are harder to phish

Imagine receiving an email that appears to come from a cloud service your company uses. The message sends you to a convincing imitation of its login page.

With a password, the fake page only needs to persuade you to type your credentials. If it also captures a one-time code, an attacker may have enough information to attempt an account takeover.

A FIDO2 credential behaves differently because it is associated with the legitimate service. Authentication involves cryptographic verification rather than handing a reusable secret to whatever page asks for it. A lookalike phishing domain therefore cannot simply collect the passkey and reuse it on the real site.

This changes an important part of security training. Employees still need to recognize suspicious messages and protect their devices, but authentication itself can provide stronger technical protection against credential phishing instead of relying entirely on the user spotting every fake login page.

What businesses should consider before moving to passkeys

Passkeys can reduce dependence on passwords, but deployment still requires planning. Businesses should first identify which applications support FIDO2 and how employees will access those applications across phones, desktops, and other devices.

Account recovery deserves particular attention. If someone loses a device, replaces a phone, or leaves the company, there needs to be a controlled way to restore legitimate access without creating a weaker recovery path that attackers can exploit.

Organizations should also decide whether synced or device-bound credentials make more sense for particular accounts. Synced passkeys can make everyday access easier across a user’s devices. Device-bound credentials, including hardware security keys, may be preferred for accounts where tighter control over the authenticator is required.

Compatibility matters as well. A company may have modern cloud applications that support passkeys alongside older software that still depends on passwords. A staged rollout can work better than attempting to eliminate every password at once. Start with services that already provide mature passkey support, document the recovery process, and make sure employees understand what they’ll see when signing in.

Login security is moving away from shared secrets

FIDO2 doesn’t make device security, access policies, or user education unnecessary. What it changes is the basic assumption that authentication must depend on a secret users repeatedly type into websites.

Passkeys move that proof into cryptographic credentials protected by devices users already carry. Biometrics can then make accessing those credentials quick and familiar without becoming a reusable secret sent across the internet.

For organizations evaluating passwordless authentication, that architectural change is the important part. The goal isn’t simply to make passwords more convenient. It’s to stop depending on passwords for authentication in the first place.